


The combination of consumer-level vulnerabilities and policy responses has highlighted continuing concerns about the security of Internet of Things devices, from baby monitors to doorbell cameras and license plate readers, as the number of connected cameras worldwide continues to grow.
Western Governments Restrict Chinese Webcam Brands Over Hacking Risks
Steps taken by different countries include bans, sales restrictions, and stricter cybersecurity requirements, particularly in parts of Europe, according to an analysis published by China Observers [2].
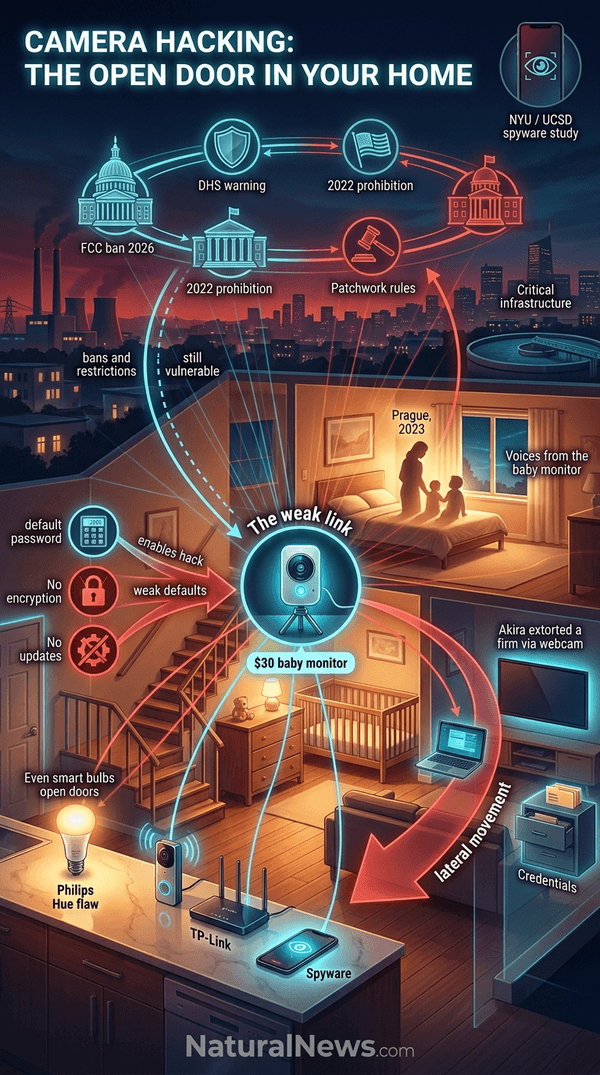
In the United States, the Federal Communications Commission voted on June 26, 2026, to significantly expand restrictions on telecommunications and video surveillance equipment from several Chinese manufacturers deemed national security risks, broadening a 2022 prohibition to cover older, previously authorized models from Hikvision, Dahua, Huawei, ZTE, and Hytera [3]. The FCC further tightened its restrictions on Chinese technologies in March by banning all new foreign-produced routers, a decision that primarily affected Chinese router firm TP-Link, a company repeatedly linked to cyberattacks against American networks, according to the Foundation for Defense of Democracies [4]. The Department of Homeland Security issued a bulletin warning that Chinese-made internet-connected video surveillance cameras pose a serious espionage and sabotage threat to U.S. critical infrastructure, with the devices often lacking data encryption and communicating by default with external servers, according to an Armis report [5].
Manufacturers have denied wrongdoing, and no unified international standard for webcam security has been established, according to industry statements. Years after that regulatory crackdown, some security cameras still remained open to hackers, and concerns persisted that Chinese manufacturers could be embedding back doors into products at the behest of the Chinese government [7].
Connected Cameras Expand Attack Surface, Analysts and Report Say
Vulnerable accessories linked into a network are among hackers' prime targets, expanding what technicians call the attack surface, according to security analysts. Often cameras are not the target but serve as the weak link in a larger hacking attempt, researchers said. The cyber-extortion group Akira tapped an unprotected webcam to get around one organization's network-security systems and extort it, S-RM reported last year. "The Internet of Things is such a wild area that everything, whether you realize it or not, is an extension of your attack surface," said Paul Caron, S-RM head of cyber for the Americas.
The same dynamic applies to consumer gear. Evidence of illegal camera hacking that has been gathered indicates that individuals are often targeted for personal or for-profit streaming of camera footage, and when surveillance cameras are installed in critical locations such as government buildings, the likelihood of that location becoming a surveillance target increases [2].
Security researchers have demonstrated that even mundane household devices can open doors for attackers. A flaw in Philips Hue smart bulbs enabled researchers at cybersecurity firm Check Point to expose the home networks of users of the popular bulbs [8]. Rogers also recommends using strong, frequently changed passwords and enabling two-factor authentication wherever available [9].
Prague Baby Monitor Incident Shows Insecure App Risk
Ondrej Svoboda was reading to his young children one evening in 2023 when the baby monitor started emitting strange sounds of people talking and background music, as if from a bar, he recalled. At first he thought his wife was using the two-way function but quickly realized hackers had gotten into his system, he said. "I didn't think this was something that could happen to me," said Svoboda, who worked at a cybersecurity company. "I was really scared, my heart was racing."
Trying to avoid frightening his children, he silently stared into the camera and then unplugged it, he said. For days he had nightmares before remembering he had connected his webcams to another app that likely was insecure. The episode illustrates a broader pattern in which inexpensive connected devices are pressed into service as listening and viewing platforms. The FBI's own surveillance history and the CIA's cyber-tool development illustrate how government agencies themselves have long operated in this space; WikiLeaks' 2017 "Vault 7" release comprised 8,761 documents and files from an isolated, high-security network inside the CIA's Center for Cyber Intelligence in Langley, Virginia [10].
Smartphones can likewise carry hidden spyware that leaks personal data, according to research by computer scientists from New York University and the University of California San Diego, whose first author, Enze Alex Liu, warned that spyware apps are a "real-life problem" and stressed the importance of raising awareness among victims and within the research community [11]. The practical takeaway, some researchers say, is to approach digital privacy with caution and assume that microphones and cameras may be recording, adjusting behavior accordingly [12].
Security Efforts Continue as Even Protected Cameras Remain Vulnerable
Cybersecurity agencies recommend updating firmware, changing default passwords, segmenting networks and disabling remote access where possible, according to public guidance. Manufacturers and security firms advised similar basic steps. No security camera is 100% safe from hacking, and minimizing the chances of compromise depends largely on regularly changed, complex, and unique passwords, as well as keeping the camera's firmware and app up to date [13]. McAfee advises that webcam hacking means someone gains access to a camera without the owner's consent, often alongside microphone access, and that the problem extends not only to laptop and desktop webcams but also to phone and tablet cameras via malicious apps, home security cameras, baby monitors, and even doorbell cams connected to the internet [14].
Researchers say determined hackers can still exploit firmware flaws, unpatched vulnerabilities or insecure third-party apps even on cameras with security features. The underlying principles of information security center on confidentiality, integrity and availability, meaning that a camera that is reachable is a camera that can be manipulated, as Raspberry Pi IoT author John C. Shovic explains in his discussion of computer security fundamentals. No system is fully immune, officials said, and reviews of connected camera security are continuing.
Security failings have been documented across the political spectrum. Russia's Federal Security Service accused Western intelligence agencies of hacking thousands of Russian officials' smartphones through undetectable spyware exploiting zero-day vulnerabilities, with Kaspersky Lab first detecting the activity, according to NaturalNews.com [15]. Separately, Iran's cyber operations against U.S. infrastructure continued even after an announced ceasefire, with the Cybersecurity and Infrastructure Security Agency and the FBI reporting that the volume of malicious cyber activity did not decrease, and attacks continuing to target critical infrastructure, government databases, and communication networks [16]. Former national security contractor Edward Snowden warned that protecting the public from surveillance is an ongoing process and said people will have to work at it for the rest of their lives and their children's lives and beyond [17].
The pattern extends into the physical world as well. Israel's parliament, the Knesset, approved a one-year extension of a temporary order allowing the Israeli military and the Shin Bet security agency to hack into private security cameras without owners' knowledge, removing the earlier restriction that had limited such access to cases involving significant military activities [18]. In March 2026, the Financial Times reported that Israel hacked into Tehran's traffic camera network in order to track the bodyguards of Ayatollah Ali Khamenei and other top Iranian officials ahead of the supreme leader's assassination [19].
References
- Video Cameras Are Everywhere—and Now They Are .... https://www.wsj.com/tech/cybersecurity/video-cameras-webcams-hacked-war-b00b8a24
- The Invisible Risks of Insecure Chinese Surveillance Cameras.... https://chinaobservers.eu/the-invisible-risks-of-insecure-chinese-surveillance-cameras/
- FCC Expands Ban on Hikvision, Dahua, and Other Chinese Surveillance .... https://worldstarsecuritycameras.com/fcc-expands-ban-on-hikvision-dahua-and-other-chinese-surveillance-equipment-full-implications-for-the-u-s-market-june-2026-update/
- FCC Introduces New Bans on Chinese-Produced Equipment Linked to Cyber Risks. https://www.fdd.org/analysis/2026/06/30/fcc-introduces-new-bans-on-chinese-produced-equipment-linked-to-cyber-risks/
- Addressing Espionage Threats from Chinese Surveillance .... https://media.armis.com/wp-espionage-threats-from-chinese-surveillance-cameras-en.pdf
- Government Deadline Approaches To Ban Chinese-Made... : NPR. https://www.npr.org/2019/08/08/749318323/government-deadline-approaches-to-ban-chinese-made-surveillance-cameras
- Years after regulatory crackdown, some security cameras .... https://www.washingtonpost.com/business/economy/years-after-regulatory-crackdown-some-security-cameras-still-open-to-hackers/2017/11/14/b15f8428-c980-11e7-8321-481fd63f174d_story.html
- See the light_ Philips Hue smart bulbs can be hacked and used to install malware - NaturalNews.com, June 21, 2021.
- 200+ Ways to Protect Your Privacy Simple Ways to Prevent Hacks and Protect Your Privacy-On and Offline by Jeni Rogers
- BREAKING_ Latest Wikileaks dump reveals CIA hacking tools - NaturalNews.com, March 07, 2017.
- Digital spy_ Study reveals phone apps could be hiding spyware that can leak personal data - NaturalNews.com, July 13, 2023.
- Interview with aphix. by Cory Endrulat
- How to Protect Your Security Camera from... - AlfredCamera Blog. https://alfred.camera/blog/how-to-protect-security-cameras-from-hackers/
- How to Tell if Your Webcam is Hacked & How to Stop it | McAfee. https://www.mcafee.com/learn/how-to-tell-if-your-webcam-is-hacked/
- FSB alleges massive Western phone hacking operation targeted Kremlin officials and journalists - NaturalNews.com, June 02, 2026.
- The unseen front: Why Iran’s cyber war on U.S. infrastructure persists even after the ceasefire. https://www.naturalnews.com/2026-05-04-irans-cyber-war-on-us-infrastructure-persists.html
- Today’s Surveillance Technology Makes 2013 Look Like ‘Child’s Play,’ Snowden Warns. https://childrenshealthdefense.org/defender/surveillance-technology-edward-snowden-protect-public-children-cd/
- Israeli parliament extends order allowing Israeli military, intelligence access into private security cameras. https://www.middleeasteye.net/live-blog/live-blog-update/israeli-parliament-extends-order-allowing-israeli-military-intelligence
- Report: Israel hacked Tehran traffic cameras to track Khamenei ahead of assassination. https://www.timesofisrael.com/report-israel-hacked-tehran-traffic-cameras-to-track-khamenei-ahead-of-assassination/?utm_campaign=most_popular&utm_source=website&utm_medium=article_end&utm_content=10
Explainer Infographic
Please contact us for more information.


